Computer Networking > EXAM REVIEW > Final Exam Review - Sheridan College INFO 24178 (All)
Final Exam Review - Sheridan College INFO 24178
Document Content and Description Below
Last updated: 3 years ago
Preview 1 out of 3 pages
Instant download
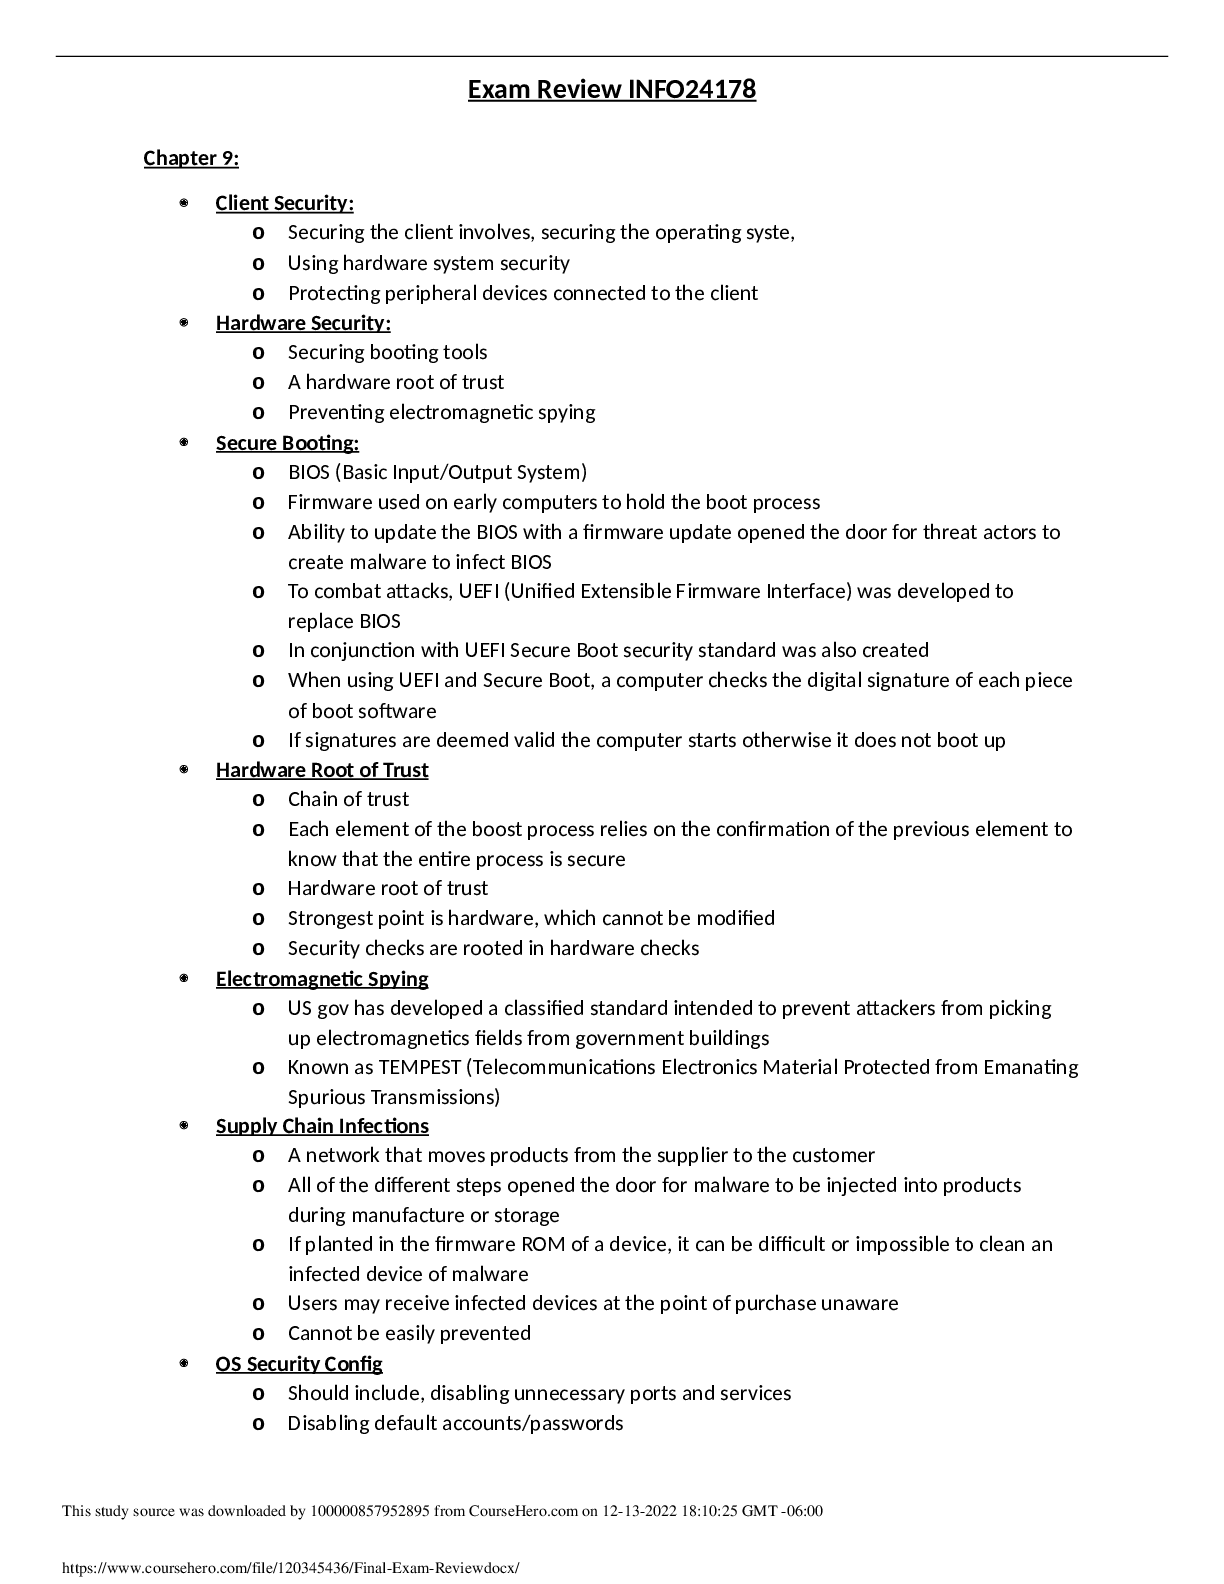
Buy this Document to get the Full Access Instantly
Provided by Students Who Aced it
We Verify Document Content to Gurantee Accuracy
Reviews( 0 )
Document information
Connected school, study & course
About the document
Uploaded On
Dec 14, 2022
Number of pages
3
Written in
All

Additional information
This document has been written for:
Uploaded
Dec 14, 2022
Downloads
0
Views
127
Topic Tags
Recommended For You
Get more on EXAM REVIEW »
Test Bank for Computer Security Fundamentals 5th Edition By Wi...
Test Bank for Computer Security Fundamentals 4th Edition By Wi...
 2022 test Bank.png)
AI-900 Microsoft Azure AI Fundamentals Certification exam test...

CSIS 330 Quiz 1 Liberty University answers complete solutions;...

MTA 98-366 Exam / MTA: IT Infrastructure, Network Infrastructu...

LIBERTY UNIVERSITY CSIS 340 Final Exam 1 QUESTIONS WITH ALL VE...
Business Data Networks and Security, 11e (Panko) Chapter 11 Ne...

ITN 277 Final Exam / Network Infrastructure & Security / 2025...
WGU D415 Software Defined Networking / SDN Certification Exam...
COM 207 | COM207 EXAM 2 STUDY GUIDE - ARIZONA STATE UNIVERSITY
Network+ N10-009 Acronyms Study Guide 2025 – CompTIA Exam Obje...

Certified Kubernetes Administrator CKA / Score 100% / New 2025...
CS6250 Exam 2 Study Guide 2025 – CN CS 6250 Comprehensive Revi...
CS6250 Exam 2 Study Guide 2025 – CN CS 6250 Comprehensive Revi...
University of Maryland, University College CMIT 350 Cisco Netw...




.png)

