Splunk Fundamentals 1 Questions and
Answers Rated A+
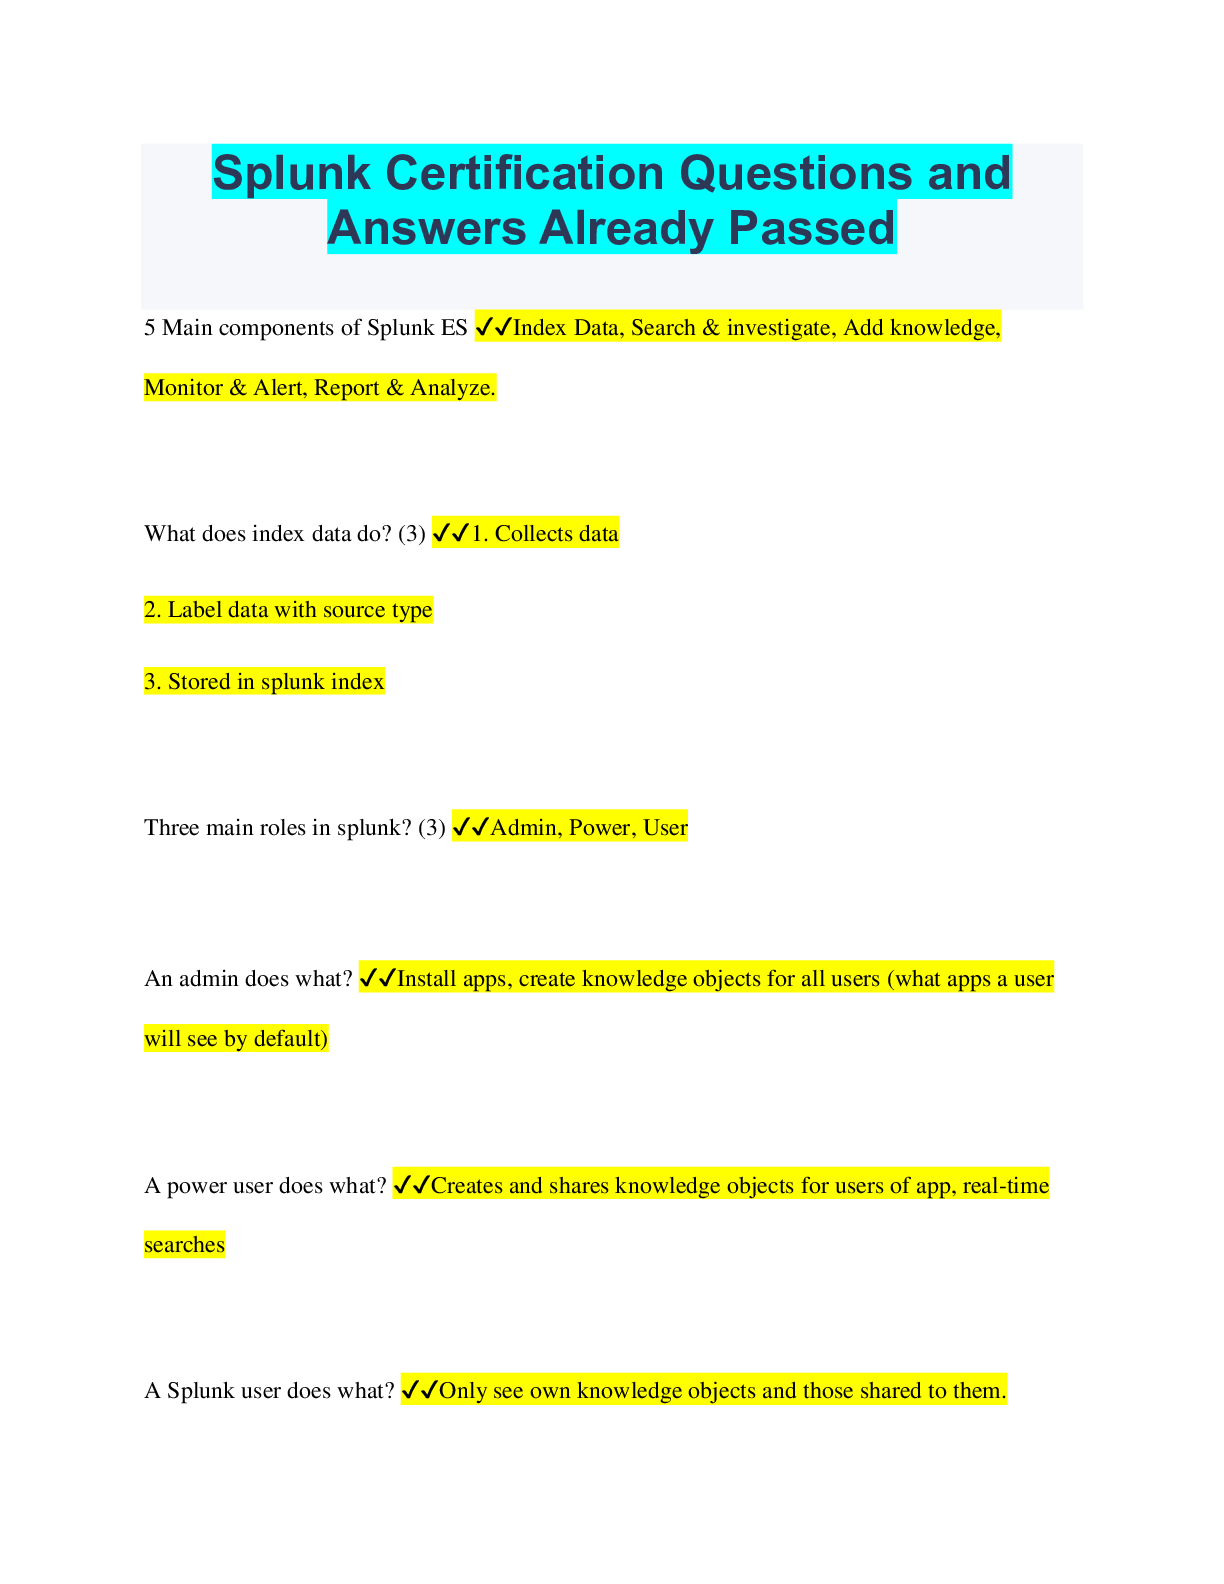
Machine data is generated by ✔✔All types of system in an organization
Structure of machine data ✔✔Unstructured
Machine data makes up ___% of data accumulated by or
...
Splunk Fundamentals 1 Questions and
Answers Rated A+
Machine data is generated by ✔✔All types of system in an organization
Structure of machine data ✔✔Unstructured
Machine data makes up ___% of data accumulated by organizations ✔✔90
Main way data is supplied for indexing ✔✔Forwarders
Search requests are processed by the ✔✔Indexers
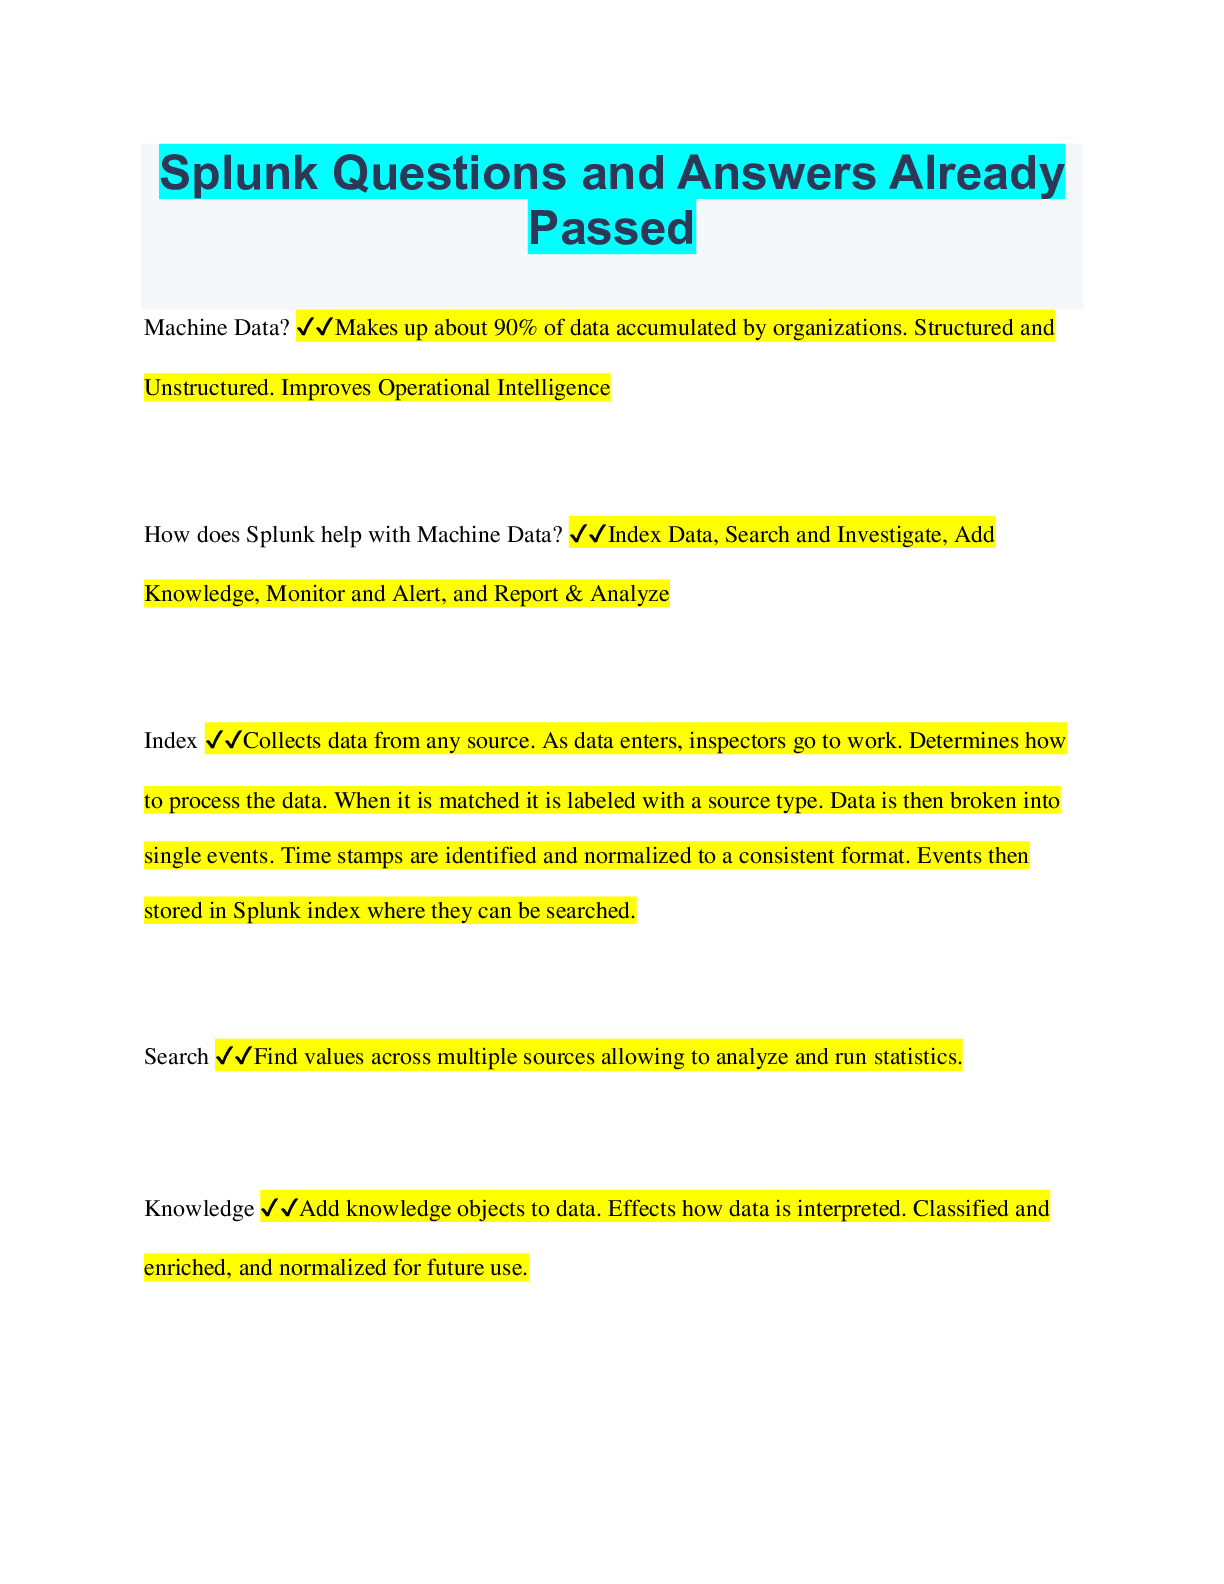
3 main components of splunk ✔✔Collect and index data
Add knowledge
Search and investigate
Single instance deployment can handle ✔✔searching
indexing
input
parsing
three main processing components ✔✔forwarders
search heads
indexers
search strings are sent from ✔✔Search Heads
Which function is not a part of single instance deployment ✔✔Clustering
The password for a new instance is ✔✔created when you install splunk
___ define what users can do in splunk ✔✔roles
What roles will only see their knowledge objects and those that have been shared with them
✔✔User
You can launch and manage apps from the home app ✔✔True
3 default roles ✔✔user
admin
power
most prod environment user ___ for source of data input ✔✔forwarders
this lets splunk know where to break the event, timestamp is located and how to auto create
fields pairs ✔✔Source types
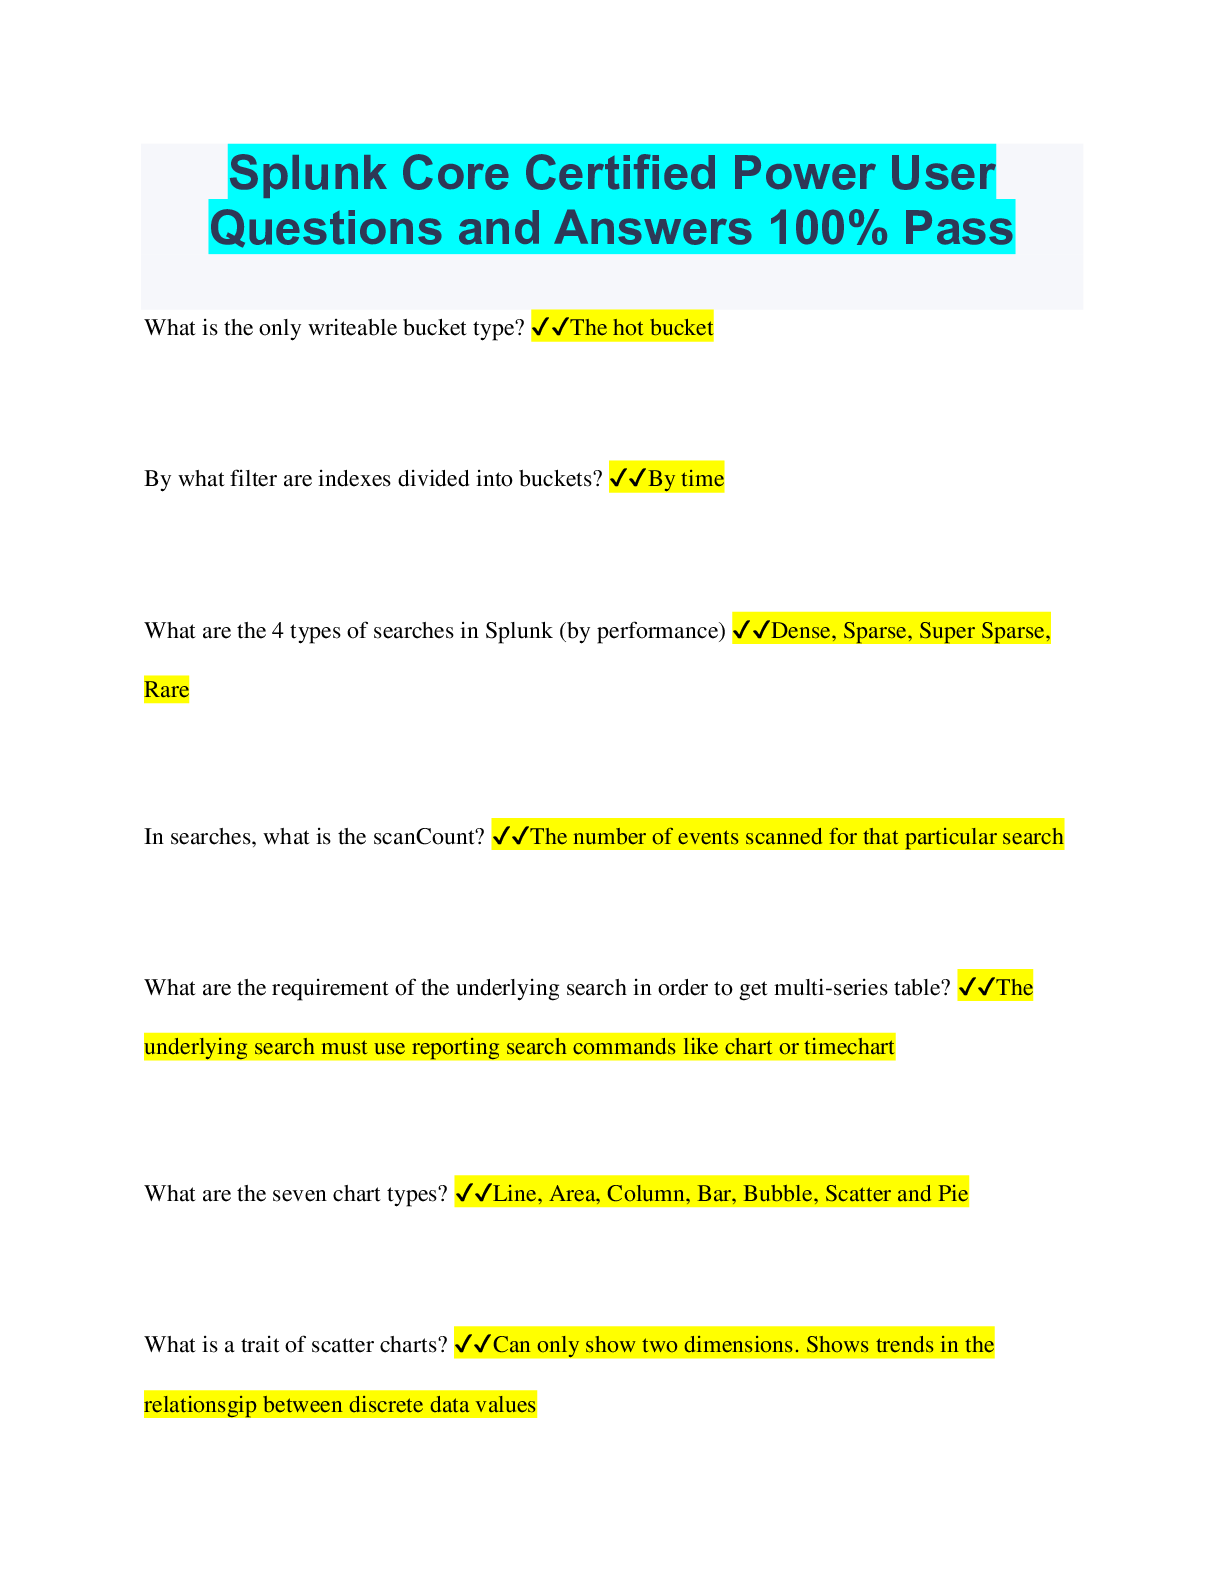
How would you continually monitor files in splunk ✔✔Monitor
Files indexed using the upload input option get indexed ✔✔Once
splunk uses source types to categorize the type of data being indexed ✔✔Source Types
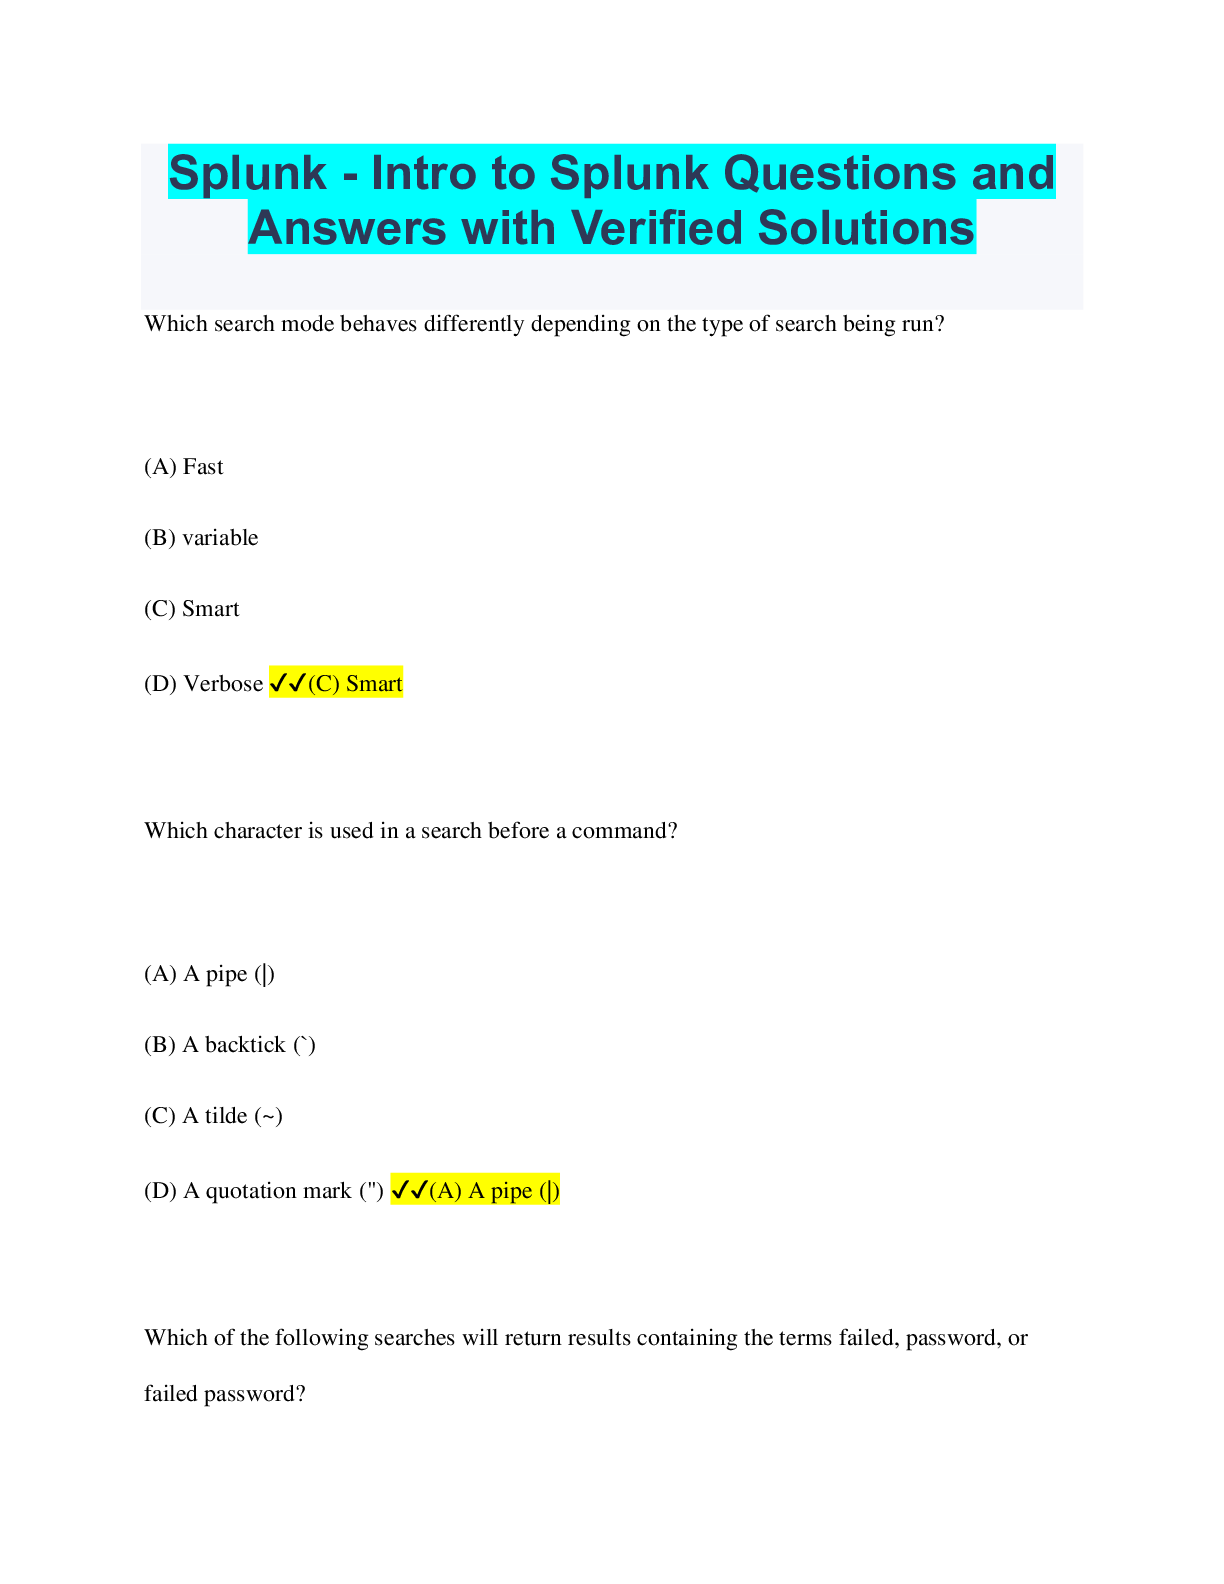
Toggles search mode by behavior ✔✔Smart mode
What order are events listed ✔✔Reverse chronological
* ✔✔wildcard
commands that create stats and visualizations are ✔✔transforming commands
when a search is sent to splunk it becomes a ✔✔search job
field VALUES are case sensitive ✔✔False
Field names are ✔✔case sensitive
Which is better inclusion or exclusion ✔✔inclusion
Most efficient way to filter events in splunk ✔✔time
Having separate indexes all these 3 things ✔✔- faster searches
- multiple retention policies
- ability to limit access
How to round down to the nearest unit of specified time ✔✔@
how to remove a field from returned events ✔✔fields -
command to remove duplicate field values ✔✔dedup
excluding fields will benefit performance ✔✔false
rename a field ✔✔rename as "NEW NAME"
how many results are shown by default with top or rare command ✔✔10
What type of search values need to be returned to view the results as a chart ✔✔Statistical values
charts are based on ✔✔numbers, time or location
time range picker in dashboard will only work on panels that include a ___ search ✔✔inline
data models are made up of ✔✔datasets
the instant pivot button is displayed in the statistics and visualization tabs when a ___ search is
run ✔✔non-transforming
Pivots can be saved a report panels ✔✔false
pivots can be saved as dashboard panels ✔✔true
adding child data model objects is like the ___ boolean in the splunk search language ✔✔AND
command to display data from lookup file ✔✔inputlookup http_status.csv
external data used by lookup can come from sources like ✔✔- csv files
- scripts
- geospatial
to keep from overwriting existing fields with your lookup you can use the ___ clause
✔✔outputnew
alert is action triggered by a ✔✔saved search
alerts can be shared to all apps ✔✔true
alerts can run uploaded scripts ✔✔true
[Show More]