Information Technology > QUESTIONS & ANSWERS > C795- Cybersecurity Management II (Tactical) Questions and Answers Already Passed (All)
C795- Cybersecurity Management II (Tactical) Questions and Answers Already Passed
Document Content and Description Below
Last updated: 3 years ago
Preview 1 out of 18 pages
Instant download
.png)
Buy this Document to get the Full Access Instantly
Provided by Students Who Aced it
We Verify Document Content to Gurantee Accuracy
Also available in bundle (1)
Click Below to Access Bundle(s)
.png)
WGU C795- Cybersecurity Management II – Tactical Bundled Exams Questions and Answers with Complete Solutions
WGU C795- Cybersecurity Management II – Tactical Bundled Exams Questions and Answers with Complete Solutions
By Nutmegs 4 years ago
$20
8
Reviews( 0 )
Document information
Connected school, study & course
About the document
Uploaded On
Aug 08, 2022
Number of pages
18
Written in
All

Additional information
This document has been written for:
Uploaded
Aug 08, 2022
Downloads
1
Views
293
Topic Tags
Recommended For You
Get more on QUESTIONS & ANSWERS ».png)
WGU C795 Cyber Security Management II Tactical Questions and A...
WGU C795 Cyber security Management II – Tactical Questions and...
.png)
Cybersecurity Management II - Tactical - C795 Ucertify Questio...
.png)
Cyber security Management II - Tactical - C795 Preassessment Q...
.png)
WGU C795- Cybersecurity Management II – Tactical Latest Update...
.png)
WGU C795- Cybersecurity Management II – Tactical Latest Update...
WGU C795- Cybersecurity Management II – Tactical Latest Update...
WGU C795- Cybersecurity Management II – Tactical Latest Update...

WGU C795 CYBER SECURITY MANAGEMENT II|WITH CORRECT ANSWERS

WGU MASTER'S COURSE C795 - CYBERSECURITY MANAGEMENT II TACTICA...

WGU Master's Course C795 - Cybersecurity Management II Tactica...
WGU C795 Cybersecurity Management II Tactical - Ucertify Extra...
Advanced Study Guide for WGU Master’s Course C795 – Cybersecur...

WGU C795 Cybersecurity Management II (Tactical) – Study Guide...
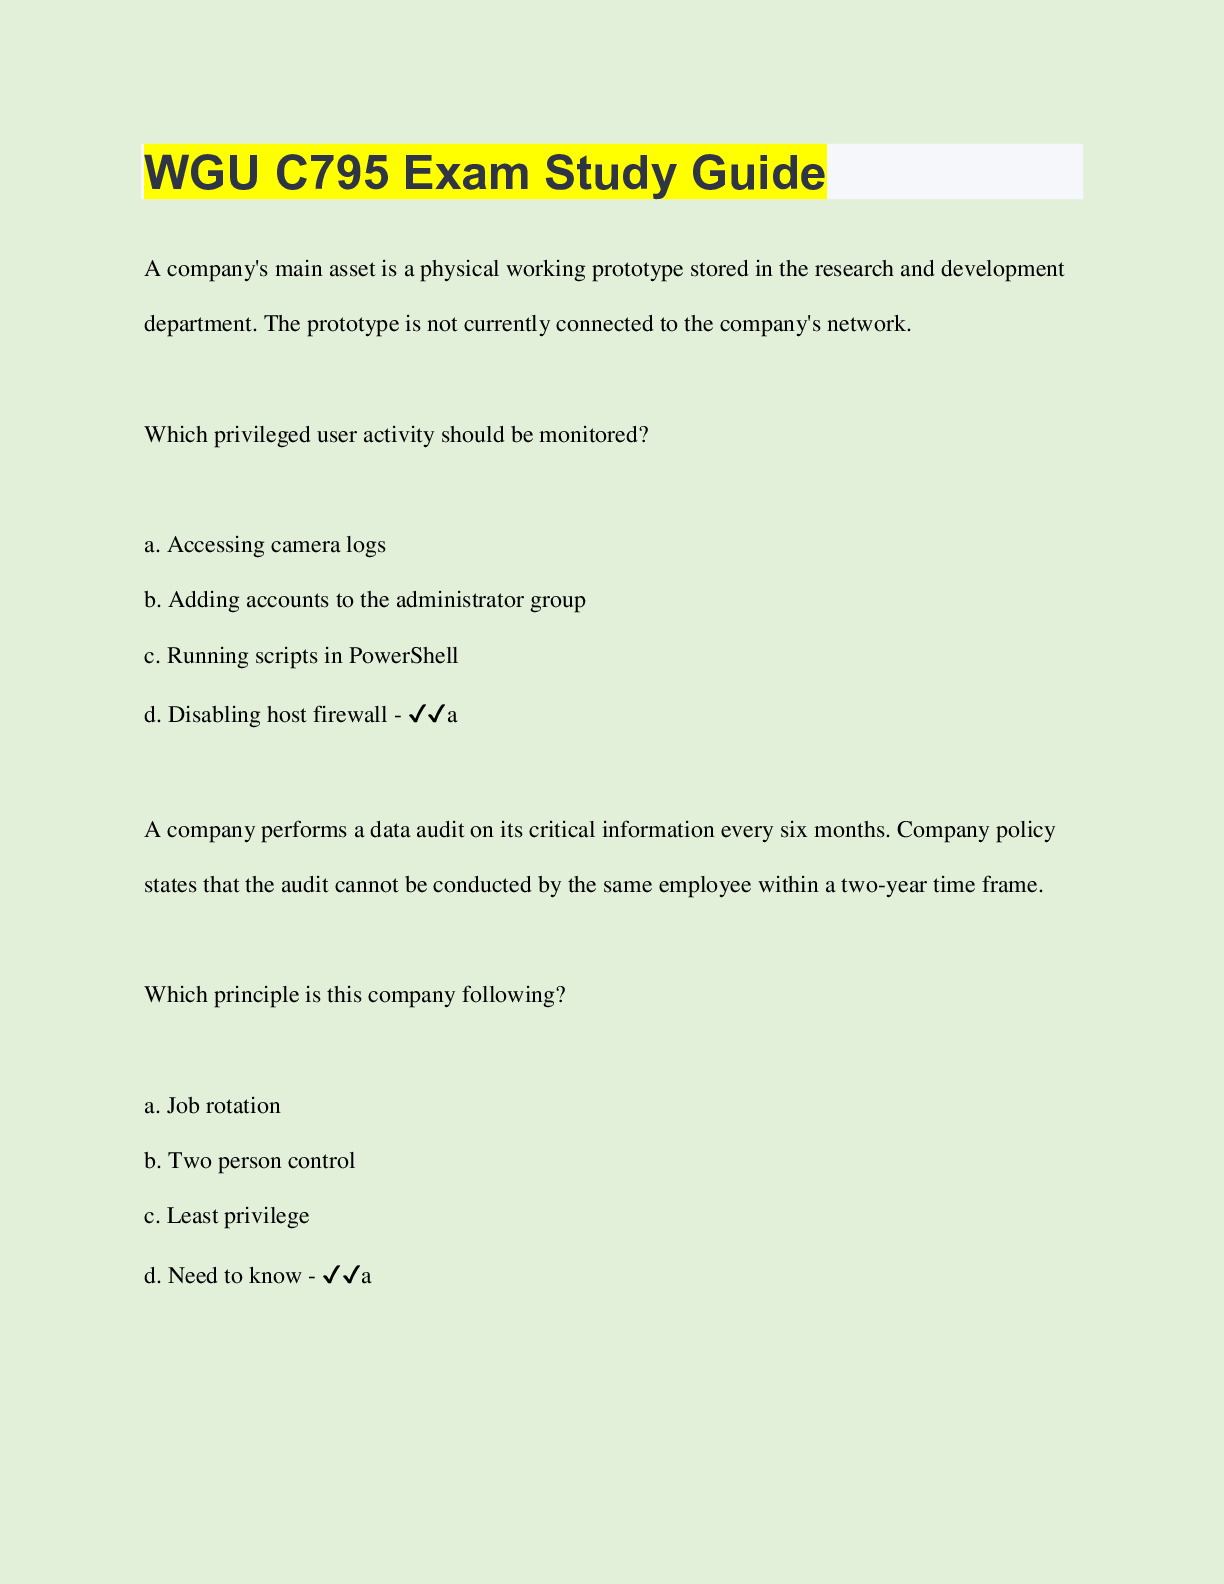
WGU C795 Exam Study Guide | Questions with 100% Correct Answe...
Information Systems What Every Business Student Needs to Know,...
.png)