Computer Networking > QUESTIONS & ANSWERS > PNSCE - Firewall 10.0: WildFire Versus Malware Exam Questions with Correct Answers (All)
PNSCE - Firewall 10.0: WildFire Versus Malware Exam Questions with Correct Answers
Document Content and Description Below
Last updated: 4 years ago
Preview 1 out of 19 pages
Instant download

Buy this Document to get the Full Access Instantly
Provided by Students Who Aced it
We Verify Document Content to Gurantee Accuracy
Also available in bundle (1)
Click Below to Access Bundle(s)

PCNSA Bundled Exams with complete solutions
PCNSA Bundled Exams with complete solutions PCNSA 2022 Questions and Answers PNSCE - PAN-OS 10 Test Questions with Complete Answers PNSCE - Firewall 10.0: WildFire Versus Malware Exam Questions...
By Professor Lynne 4 years ago
$15
9
Reviews( 0 )
Document information
Connected school, study & course
About the document
Uploaded On
Sep 05, 2022
Number of pages
19
Written in
All

Additional information
This document has been written for:
Uploaded
Sep 05, 2022
Downloads
0
Views
203
Topic Tags
Related Subjects & Courses
Explore similar study resources and related concepts.
Recommended For You
Get more on QUESTIONS & ANSWERS »

CSIS 330 Quiz 1 Liberty University answers complete solutions;...
CSIS 330 Quiz 2 Liberty University answers complete solutions,...

MTA 98-366 Exam / MTA: IT Infrastructure, Network Infrastructu...

LIBERTY UNIVERSITY CSIS 340 Final Exam 1 QUESTIONS WITH ALL VE...

ITN 277 Final Exam / Network Infrastructure & Security / 2025...
WGU D415 Software Defined Networking / SDN Certification Exam...
Test Bank for Computer Security Fundamentals 5th Edition By Wi...
Test Bank for Computer Security Fundamentals 4th Edition By Wi...

Certified Kubernetes Administrator CKA / Score 100% / New 2025...
University of Maryland, University College CMIT 350 Cisco Netw...

University of Maryland, University College CMIT 350 Cisco Netw...
.png)
COM 207 | COM207 EXAM 2 STUDY GUIDE - ARIZONA STATE UNIVERSITY
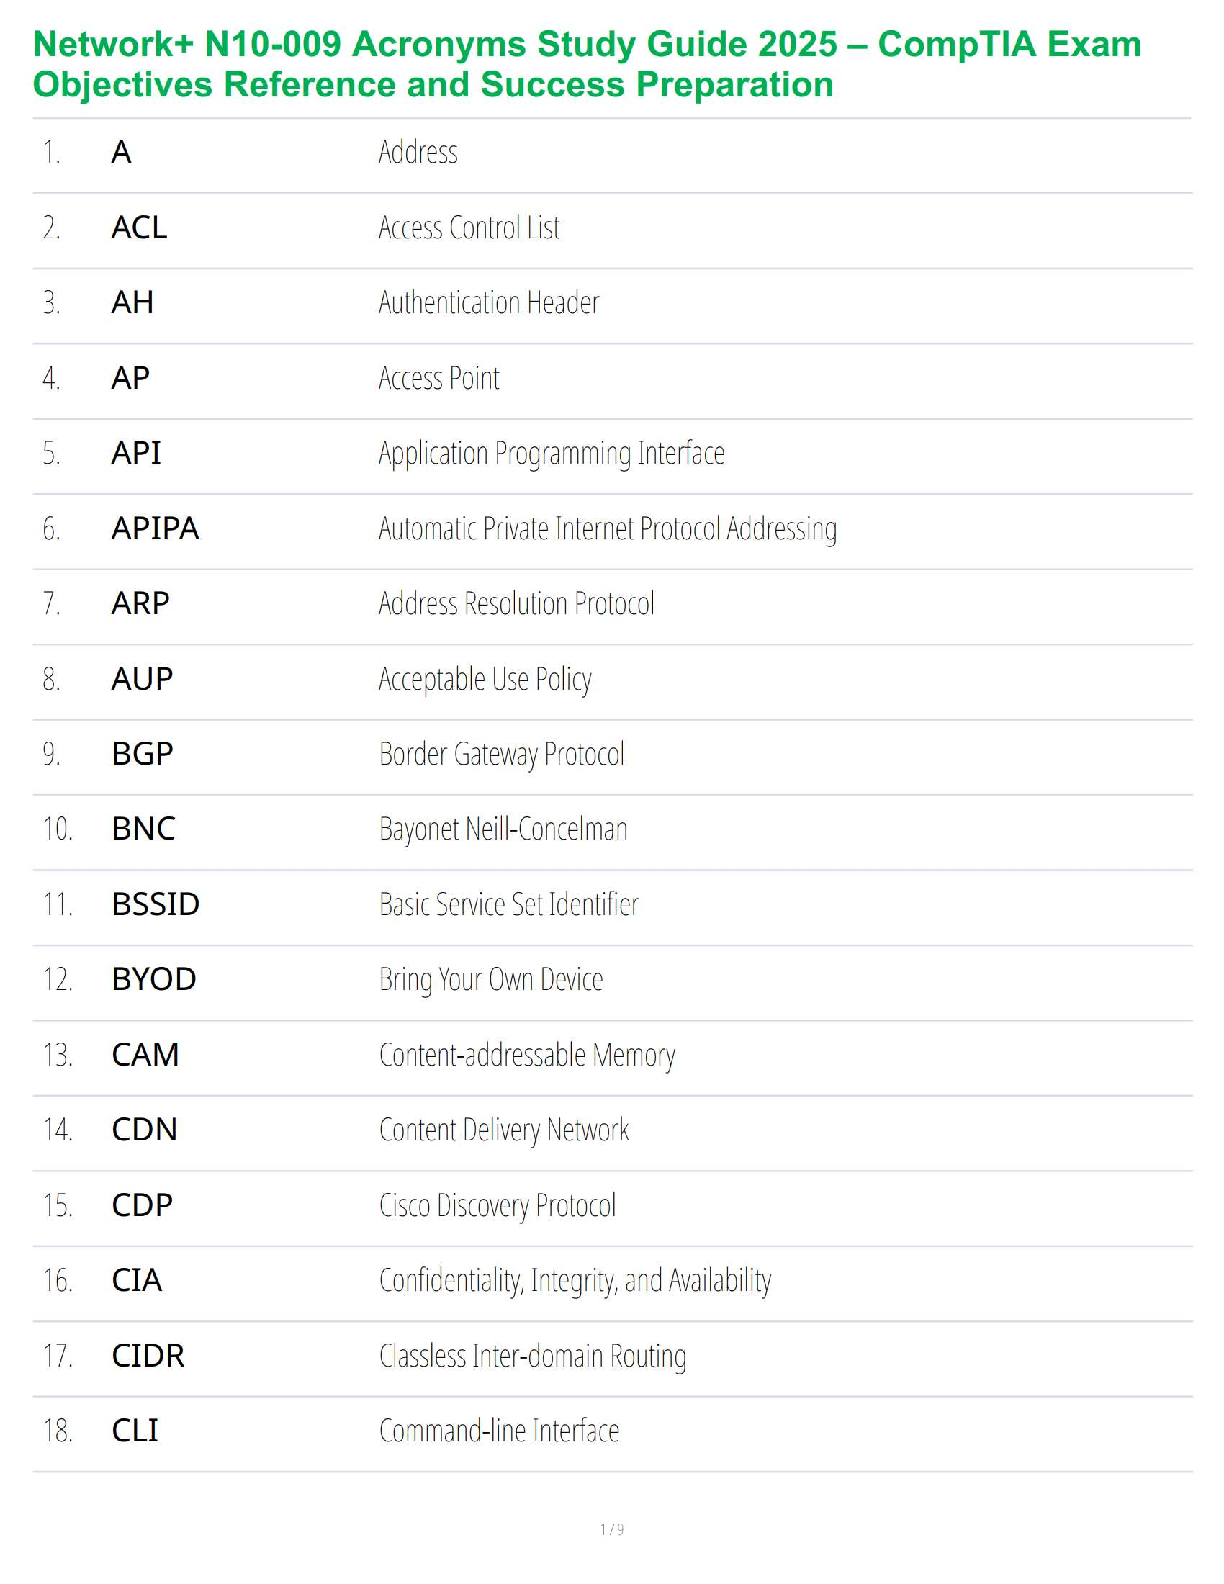
Network+ N10-009 Acronyms Study Guide 2025 – CompTIA Exam Obje...