WGU C836 MULTI/COMPREHENSIVE
FINAL EXAM REVIEW, Top Questions
and answers, rated A+
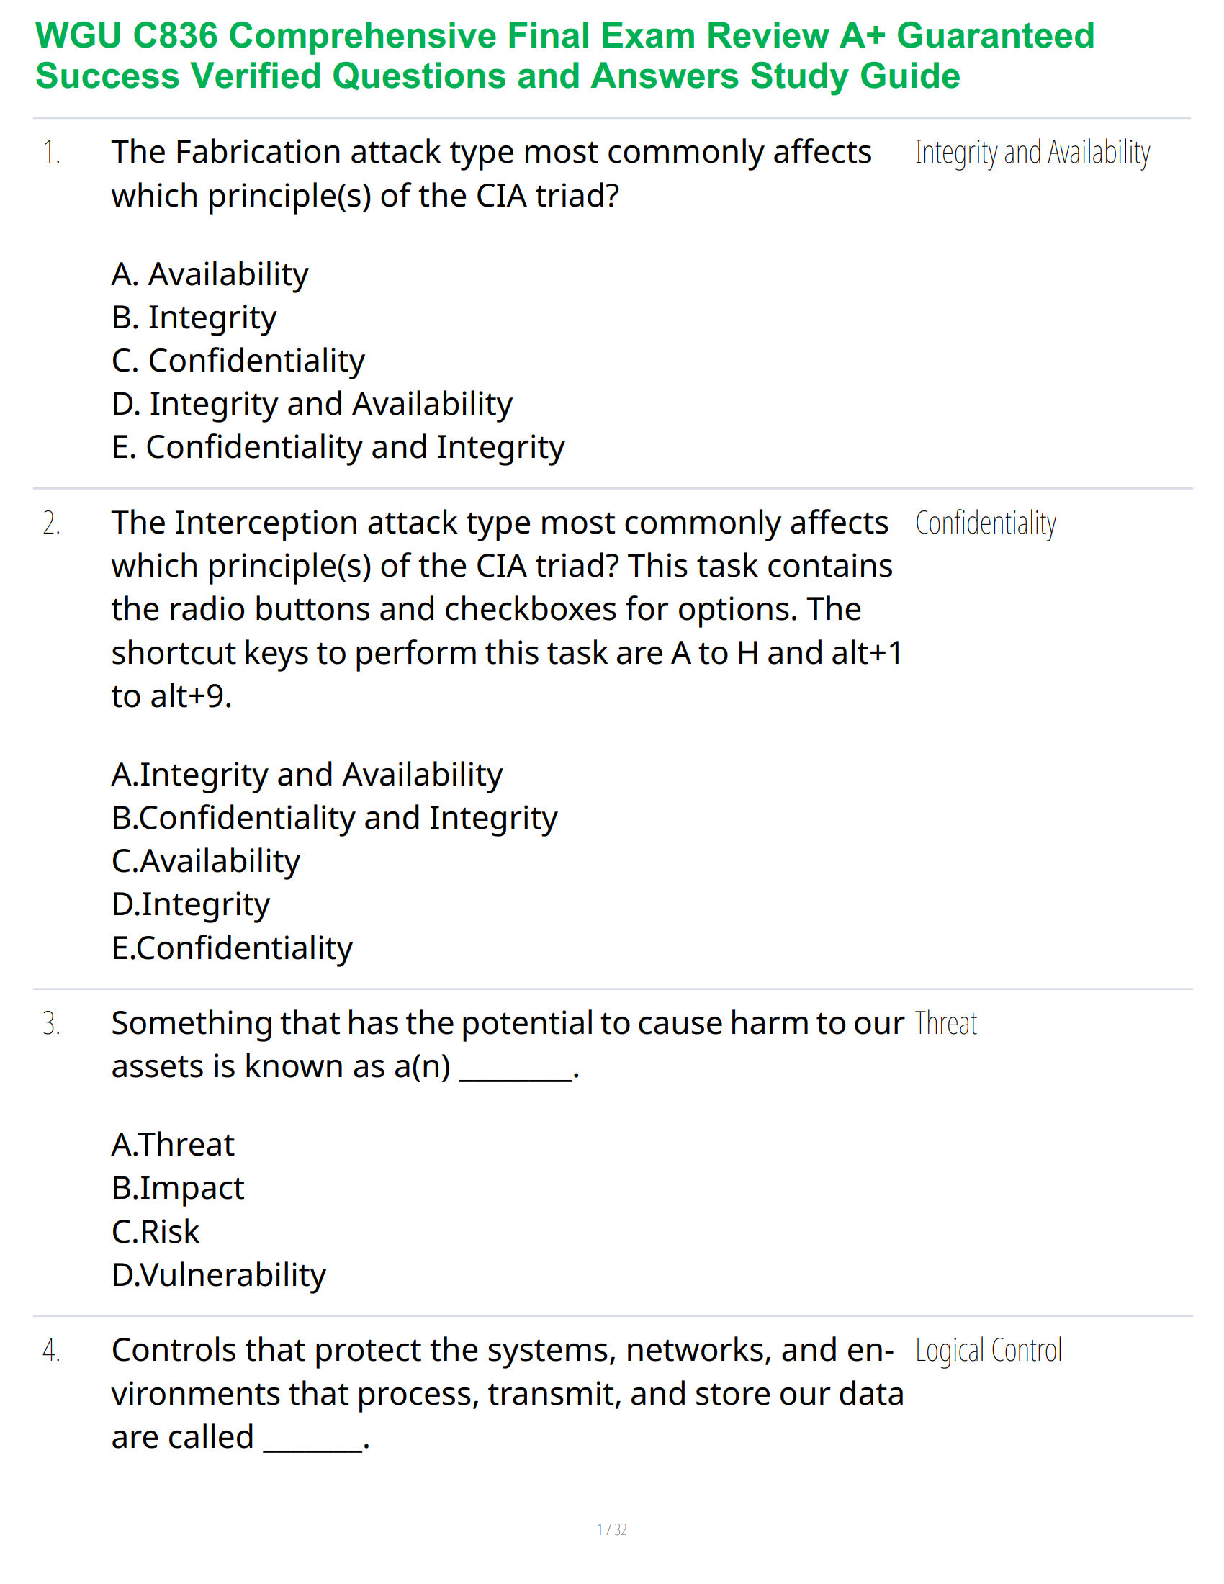
The Fabrication attack type most commonly affects which principle(s) of the CIA triad?
A. Availability
B. Integrity
C. Confident
...
WGU C836 MULTI/COMPREHENSIVE
FINAL EXAM REVIEW, Top Questions
and answers, rated A+
The Fabrication attack type most commonly affects which principle(s) of the CIA triad?
A. Availability
B. Integrity
C. Confidentiality
D. Integrity and Availability
E. Confidentiality and Integrity - ✔✔-Integrity and Availability
The Interception attack type most commonly affects which principle(s) of the CIA triad? This task
contains the radio buttons and checkboxes for options. The shortcut keys to perform this task are A to H
and alt+1 to alt+9.
A.Integrity and Availability
B.Confidentiality and Integrity
C.Availability
D.Integrity
E.Confidentiality - ✔✔-Confidentiality
Something that has the potential to cause harm to our assets is known as a(n) ________.
A.Threat
B.Impact
C.Risk
D.Vulnerability - ✔✔-Threat
Controls that protect the systems, networks, and environments that process, transmit, and store our
data are called _______.
A.Logical controls
B.Administrative controls
C.Physical controls - ✔✔-Logical Control
What is the first and arguably one of the most important steps of the risk management process?
A.Assess risks
B.Mitigate risks
C.Identify threats
D.Assess vulnerabilities
E.Identify assets - ✔✔-Identify assets
Protects information and information systems from unauthorized access, use, disclosure, disruption,
modification, or destruction - ✔✔-information security
A type of attack, primarily against confidentiality - ✔✔-Interception
Something that has the potential to cause harm to our assets - ✔✔-Threat
A weakness that can be used to harm us - ✔✔-Vulnerability
The likelihood that something bad will happen - ✔✔-Risk
An attack that involves tampering with our assets - ✔✔-Modification attack
A model that adds three more principles to the CIA triad: possession or control, utility, and authenticity -
✔✔-Parkerian hexad
The physical disposition of the media on which the data is stored - ✔✔-Possession or control
An attack that involves generating data, processes, communications, or other similar activities with a
system - ✔✔-Fabrication attack
A multilayered defense that will allow us to achieve a successful defense should one or more of our
defensive measures fail - ✔✔-Defense in depth
Sometimes called technical controls, these protect the systems, networks, and environments that
process, transmit, and store our data - ✔✔-Logical controls
Controls that protect the physical environment in which our systems sit, or where our data is stored -
✔✔-Physical controls
The risk management phase that consists of all of the activities that we can perform in advance of the
incident itself, in order to better enable us to handle it - ✔✔-Preparation phase
The risk management phase where we detect the occurrence of an issue and decide whether it is
actually an incident so that we can respond to it appropriately - ✔✔-Detection and analysis phase
The biometric characteristic that measures how well a factor resists change over time and with
advancing age is called __________.
A. Collectability
B. Acceptability
C.Universality
D.Uniqueness
E.Permanence - ✔✔-E.Permanence
What type of authentication can prevent a man-in-the-middle attack? This task contains the radio
buttons and checkboxes for options.
A.Multifactor
B.Mutual
C.Something you know
D.Something you are
ESomething you do - ✔✔-B.Mutual
An authentication mechanism in which both parties authenticate each other - ✔✔-Mutual
authentication
Describes the ease with which a system can be tricked by a falsified biometric identifier - ✔✔-
Circumvention
A user who creates a network share and sets permissions on that share is employing which model of
access control? This task contains the radio buttons and checkboxes for options. The shortcut keys to
perform this task are A to H and alt+1 to alt+9.
A. Mandatory access control
B. Discretionary access control
C. Attribute-based access control
D. Role-based access control - ✔✔-Discretionary access control
What type of access control can prevent the confused deputy problem? This task contains the radio
buttons and checkboxes for options. The shortcut keys to perform this task are A to H and alt+1 to alt+9.
A.ACLs
B.A password policy
C.Capability-based security
D.A locked door - ✔✔-Capability-based security
Confidential Services Inc. is a military-support branch consisting of 1,400 computers with Internet access
and 250 servers. All employees are required to have security clearances. From the options listed below,
what access control model would be most appropriate for this organization? This task contains the radio
buttons and checkboxes for options. The shortcut keys to perform this task are A to H and alt+1 to alt+9.
A.Discretionary access control
B.Role-based access control
C.Attribute-based access control
D.Mandatory access control - ✔✔-D.Mandatory access control
A VPN connection that is set to time out after 24 hours is demonstrating which model of access control?
This task contains the radio buttons and checkboxes for options. The shortcut keys to perform this task
are A to H and alt+1 to alt+9.
A.Mandatory access control
B.Role-based access control
C.Attribute-based access control
D.Discretionary access control - ✔✔-Attribute-based access control
Lesson: Authorization and Access Control
Objective: More Advanced
States that we should allow only the bare minimum access required in order for a given party (person,
user account, or process) to perform a needed functionality - ✔✔-Principle of least privilege
Typically built to a certain resource, these contain the identifiers of the party allowed to access the
resource and what the party is allowed to do. - ✔✔-Access control lists (ACLs)
In this method of security, a person's capabilities are oriented around the use of a token that controls
their access (e.g. a personal badge) - ✔✔-Capability-based security
A type of attack that is more common in systems that use ACLs rather than capabilities - ✔✔-The
confused deputy problem
A type of attack that misuses the authority of the browser on the user's computer - ✔✔-Cross-site
request forgery (CSRF)
Access is determined by the owner of the resource in question - ✔✔-Discretionary access control (DAC)
Similar to MAC in that access controls are set by an authority responsible for doing so, rather than by
the owner of the resource. In this model, access is based on the role the individual is performing - ✔✔-
Role-based access control (RBAC)
Access is based on attributes (of a person, a resource, or an environment) - ✔✔-Attribute-based access
control
Designed to prevent conflicts of interest; commonly used in industries that handle sensitive data. Three
main resource classes are considered in this model: objects, company groups, and conflict classes. - ✔✔-
The Brewer and Nash model
A combination of DAC and MAC, primarily concerned with the confidentiality of the resource. Two
security properties define how information can flow to and from the resource: the simple security
property and the * property. - ✔✔-The Bell-LaPadula model
Primarily concerned with protecting the integrity of data, even at the expense of confidentiality. Two
security rules: the simple integrity axiom and the * integrity axiom. - ✔✔-The Biba model
An access control model that includes many tiers of security and is used extensively by military and
government organizations and those that handle data of a very sensitive nature - ✔✔-Multilevel access
control model
What process ensures compliance with applicable laws, policies, and other bodies of administrative
control, and detects misuse? This task contains the radio buttons and checkboxes for options. The
shortcut keys to perform this task are A to H and alt+1 to alt+9.
A.Nonrepudiation
B.Deterrence
C.Auditing
D.Accountability
E.Authorization - ✔✔-C.Auditing
Lesson: Auditing and Accountability
Objective: Introduction
Nessus is an example of a(n) _______________ tool. This task contains the radio buttons and
checkboxes for options. The shortcut keys to perform this task are A to H and alt+1 to alt+9.
A.Fuzzing
B.Anti-virus
C.Anti-malware
D.Vulnerability scanning
E.Penetration testing - ✔✔-D.Vulnerability scanning
A surveillance video log contains a record, including the exact date and time, of an individual gaining
access to his company's office building after hours. He denies that he was there during that time, but the
existence of the video log proves otherwise. What benefit of accountability does this example
demonstrate? This task contains the radio buttons and checkboxes for options. The shortcut keys to
perform this task are A to H and alt+1 to alt+9.
A.Deterrence
B.Nonrepudiation
C.Intrusion detection and prevention
D.Authentication
E.Authorization - ✔✔-B.Nonrepudiation
_______ provides us with the means to trace activities in our environment back to their source. This task
contains the radio buttons and checkboxes for options. The shortcut keys to perform this task are A to H
and alt+1 to alt+9.
A.Access
B.Authentication
C.Accountability
D.Authorization
E.Nonrepudiation - ✔✔-C.Accountability
Backordered Parts is a defense contractor that builds communications parts for the military. The
employees use mostly Web-based applications for parts design and information sharing. Due to the
sensitive nature of the business, Backordered Parts would like to implement a solution that secures all
browser connections to the Web servers. What encryption solution best meets this company's needs?
This task contains the radio buttons and checkboxes for options.
A.Elliptic Curve Cryptography (ECC)
B.Digital signatures
C.Advanced Encryption Standard (AES)
D.Blowfish - ✔✔-A.Elliptic Curve Cryptography (ECC)
Lesson: Cryptography
Objective: Alert!
Question 3 : We are somewhat limited in our ability to protect which type of data? This task contains the
radio buttons and checkboxes for options. The shortcut keys to perform this task are A to H and alt+1 to
alt+9.
A.Data at rest
B.Data in motion
C.Data in use - ✔✔-C.Data in use
he science of breaking through encryption is known as _____. This task contains the radio buttons and
checkboxes for options. The shortcut keys to perform this task are A to H and alt+1 to alt+9.
A.Ciphertext
B.Cryptology
C.Cryptography
D.Cryptanalysis - ✔✔-D.Cryptanalysis
The specifics of the process used to encrypt the plaintext or decrypt the ciphertext - ✔✔-Cryptographic
algorithm
Also known as private key cryptography, this uses a single key for both encryption of the plaintext and
decryption of the ciphertext - ✔✔-Symmetric key cryptography
Example: AES
A type of cipher that takes a predetermined number of bits in the plaintext message (commonly 64 bits)
and encrypts that block - ✔✔-Block cipher
A type of cipher that encrypts each bit in the plaintext message, 1 bit at a time - ✔✔-Stream cipher
A set of symmetric block ciphers endorsed by the US government through NIST. Shares the same block
modes that DES uses and also includes other modes such as XEX-based Tweaked CodeBook (TCB) mode -
✔✔-AES
Also known as public key cryptography, this method uses two keys: a public key and a private key. - ✔✔-
Asymmetric key cryptography
Uses the RSA algorithm, an asymmetric algorithm, to secure web and email traffic - ✔✔-Secure Sockets
Layer (SSL) protocol
Also referred to as message digests, these functions do
[Show More]




.png)