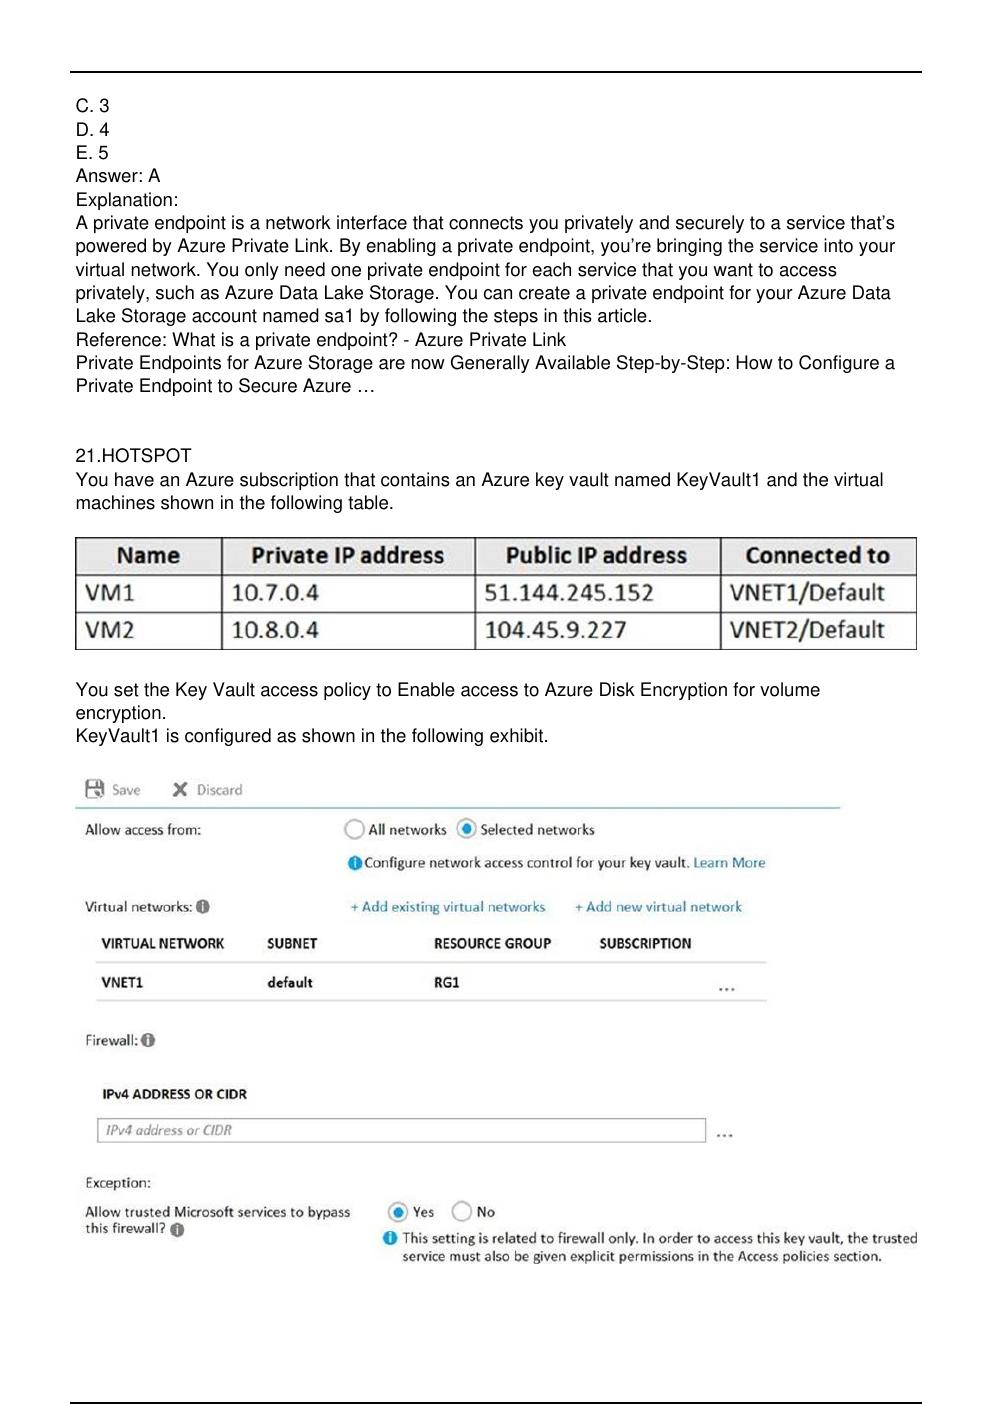
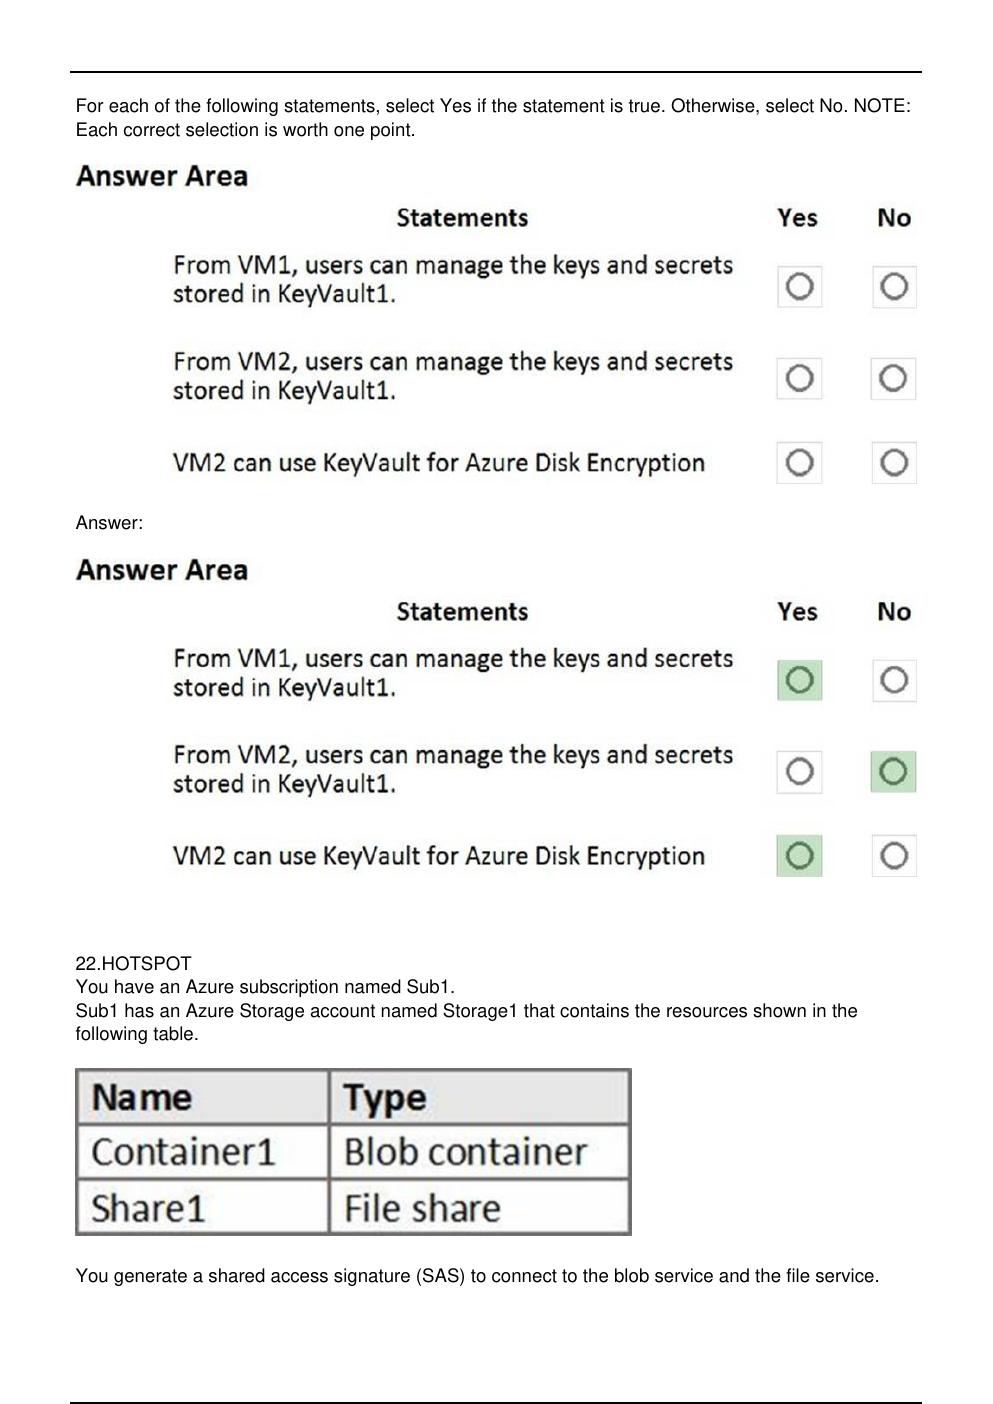
AZ-500 Exam Practice Questions
This AZ-500 exam PDF provides detailed practice questions, answers, and
explanations. These Microsoft AZ-500 exam practice questions are designed for
IT professionals, system administrat
...
AZ-500 Exam Practice Questions
This AZ-500 exam PDF provides detailed practice questions, answers, and
explanations. These Microsoft AZ-500 exam practice questions are designed for
IT professionals, system administrators, and students preparing for Microsoft Azure certification.
Key Features
Exam-Oriented Questions: Realistic practice questions that mirror the format
and difficulty of actual certification exams.
Wide Coverage: Includes cloud computing, networking, security, AI, and
enterprise IT management exams.
Study-Friendly Format: Organized sections by exam type, enabling focused
preparation.
Important Note:
This material is for personal study purposes only. Please do not
redistribute or use for commercial purposes without permission.
Share some AZ-500 exam online questions below.
1.) cannot perform write operation because following scope(s) are locked:
'subscriptions/xxxx/resourceGroups/xxx' Please remove the lock and try again.
2.SIMULATION
Lab Task
Task 3
You need to ensure that a user named Danny-31330471 can sign in to any SQL database on a
Microsoft SQL server named web31330471 by using SQL Server Management Studio (SSMS) and
Azure AD credentials.
Answer:
Create and register an Azure AD application. You can use the Azure portal, Azure PowerShell, or the
Azure CLI to do this. You need to specify a name, such as SQLServerCTP1, and select the supported
account types, such as Accounts in this organization directory only.
Grant application permissions. You can use the Azure portal, Azure PowerShell, or the Azure CLI to
do this. You need to assign the Directory.Read.All permission to the application and grant admin
consent for your organization.
Create and assign a certificate. You can use the Azure portal, Azure PowerShell, or the Azure CLI to
do this. You need to create a self-signed certificate and upload it to the application. You also need to
store the certificate in Azure Key Vault and grant access policies to the application and your SQL
Server.
Configure Azure AD authentication for SQL Server through Azure portal. You can use the Azure
portal to do this. You need to select your SQL Server resource and enable Azure AD authentication.
You also need to select your Azure AD application as the Azure AD admin for your SQL Server.
Create logins and users. You can use SSMS or Transact-SQL to do this. You need to connect to your
SQL Server as the Azure AD admin and create a login for Danny-31330471. You also need to create
a user for Danny-31330471 in each database that he needs access to.
Connect with a supported authentication method. You can use SSMS or SqlClient to do this. You
need to specify the Authentication connection property in the connection string as Active Directory
Password or Active Directory Integrated. You also need to provide the username and password of
Danny-31330471.
3.You have a multi-cloud environment that contains the following resources:
• An Azure subscription
• A Google Cloud Platform (GCP) project
• An Amazon Web Services (AWS} account
You need to use Microsoft Defender for Cloud to assign a regulatory standard that will improve the
security posture.
Which regulatory standard can be applied to all cloud environments?
A. Center for Internet Security (CIS)
B. NIST 800-53
C. System and Organization Controls (SOC) 2 Type 2
D. ISO 27001
Answer: D
4. Sign in to the Azure portal as a Global Administrator of your directory.
You must be a Global Administrator with an organizational account (for example, @yourdomain.com),
not a Microsoft account (for example, @outlook.com), to enable PIM for a directory.
Scenario: Technical requirements include: Enable Azure AD Privileged Identity Management (PIM) for
contoso.com
Reference: https://docs.microsoft.com/bs-latn-ba/azure/active-directory/privileged-identitymanagement/pim-getting-started
5. Data Discovery & Classification
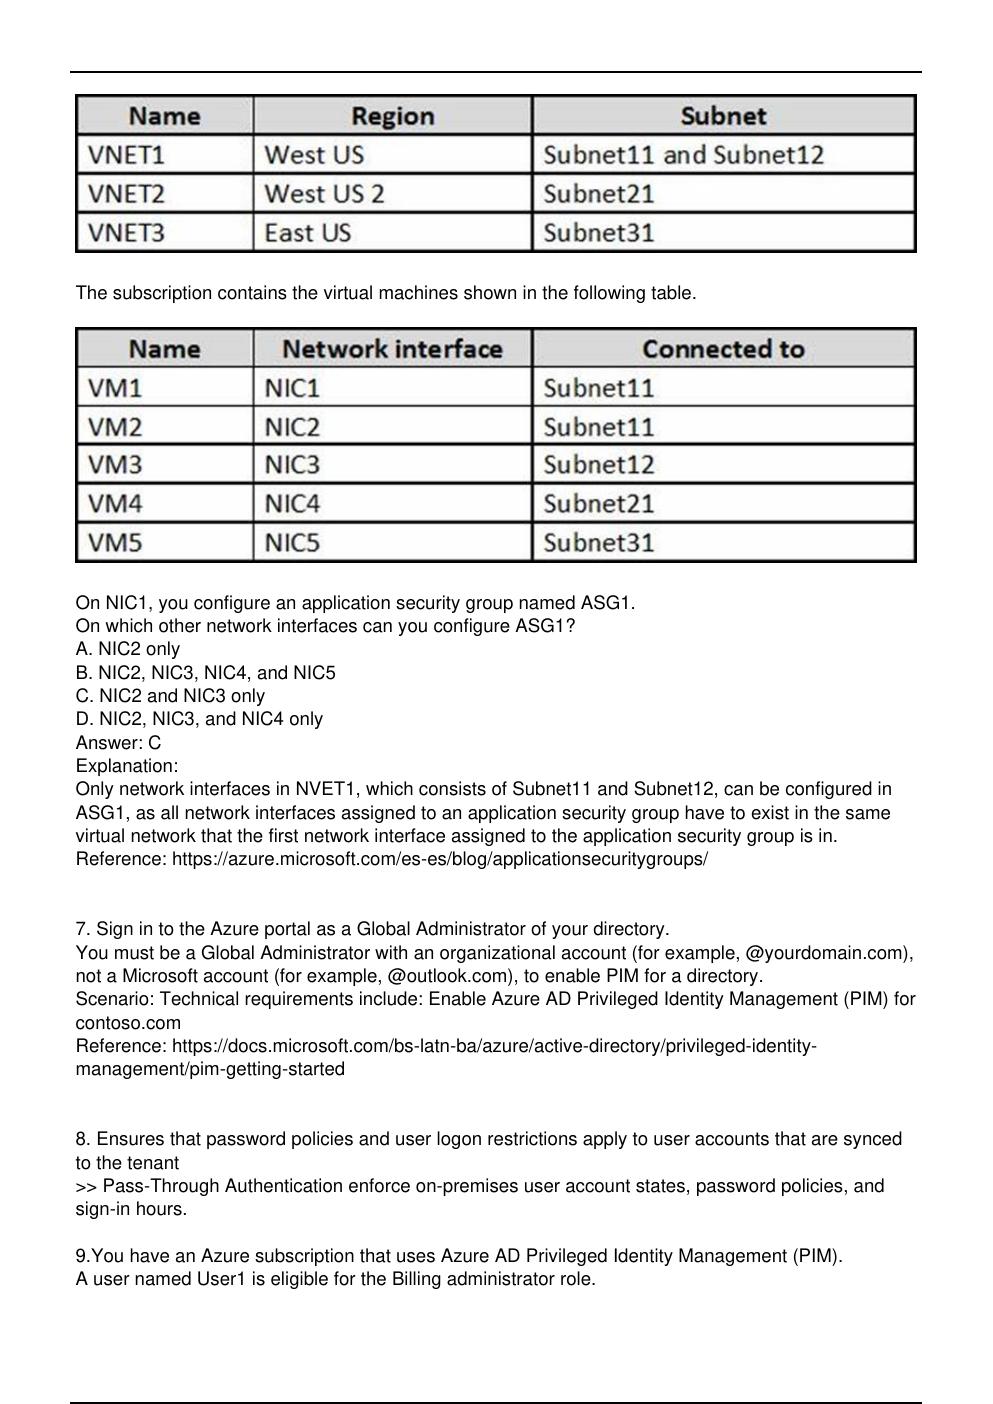
6.You have an Azure subscription that contains the virtual networks shown in the following table.
The subscription contains the virtual machines shown in the following table.
On NIC1, you configure an application security group named ASG1.
On which other network interfaces can you configure ASG1?
A. NIC2 only
B. NIC2, NIC3, NIC4, and NIC5
C. NIC2 and NIC3 only
D. NIC2, NIC3, and NIC4 only
Answer: C
Explanation:
Only network interfaces in NVET1, which consists of Subnet11 and Subnet12, can be configured in
ASG1, as all network interfaces assigned to an application security group have to exist in the same
virtual network that the first network interface assigned to the application security group is in.
Reference: https://azure.microsoft.com/es-es/blog/applicationsecuritygroups/
7. Sign in to the Azure portal as a Global Administrator of your directory.
You must be a Global Administrator with an organizational account (for example, @yourdomain.com),
not a Microsoft account (for example, @outlook.com), to enable PIM for a directory.
Scenario: Technical requirements include: Enable Azure AD Privileged Identity Management (PIM) for
contoso.com
Reference: https://docs.microsoft.com/bs-latn-ba/azure/active-directory/privileged-identitymanagement/pim-getting-started
8. Ensures that password policies and user logon restrictions apply to user accounts that are synced
to the tenant
>> Pass-Through Authentication enforce on-premises user account states, password policies, and
sign-in hours.
9.You have an Azure subscription that uses Azure AD Privileged Identity Management (PIM).
A user named User1 is eligible for the Billing administrator role.
You need to ensure that the role can only be used for a maximum of two hours.
What should you do?
A. Create a new access review.
B. Edit the role assignment settings.
C. Update the end date of the user assignment
D. Edit the role activation settings.
Answer: B
10.You have an Azure subscription that contains an Azure key vault.
You need to configure maximum number of days for Which new keys are valid. The solution must
minimize administrative effort.
What should you use?
A. Key Vault properties
B. Azure Policy
C. Azure Purview
D. Azure Blueprints
Answer: B
11.You need to delegate a user to implement the planned change for Defender for Cloud.
The solution must follow the principle of least privilege.
Which user should you choose?
A. Admin1
B. Admin2
C. Admin3
D. Admin4
Answer: B
12.SIMULATION
Lab Task
use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password. place your cursor in the Enter password box and click on the password
below.
Azure Username: User1
[email protected]
Azure Password: GpOAe4@lDg
If the Azure portal does not load successfully in the browser, press CTRL-K to reload the portal in a
new browser tab.
The following information is for technical support purposes only:
Lab Instance: 28681041
Task 9
You need to ensure that the rg1lod28681041n1 Azure Storage account is encrypted by using a key
stored in the KeyVault28681041 Azure key vault.
Answer:
To ensure that the rg1lod28681041n1 Azure Storage account is encrypted by using a key stored in
the KeyVault28681041 Azure key vault, you can follow these steps:
In the Azure portal, search for and select the storage account named rg1lod28681041n1.
In the left pane, select Encryption.
In the Encryption pane, select Customer-managed key.
In the Customer-managed key pane, select Select from Key Vault. In the Select from Key Vault pane,
enter the following information: Key vault: Select the KeyVault28681041 Azure key vault. Key: Select
the key you want to use.
Select Save.
13.You have an Azure subscription linked to an Azure Active Directory Premium Plan 1 tenant.
You plan to implement Azure Active Directory (Azure AD) Identity Protection.
You need to ensure that you can configure a user risk policy and a sign-in risk policy.
What should you do first?
A. Purchase Azure Active Directory Premium Plan 2 licenses for all users.
B. Register all users for Azure Multi-Factor Authentication (MFA).
C. Enable security defaults for Azure AD.
D. Upgrade Azure Security Center to the standard tier.
Answer: A
Explanation:
Reference: https://docs.microsoft.com/en-us/azure/active-directory/authentication/tutorial-risk-basedsspr-mfa
14.You need to implement the planned change for WAF1.
The solution must minimize administrative effort
What should you do?
A. Create an Azure policy.
B. Modify the Azure-managed DRS.
C. Add a custom rule.
D. Modify the Bot Manager 1.1 rule set.
Answer: C
15.HOTSPOT
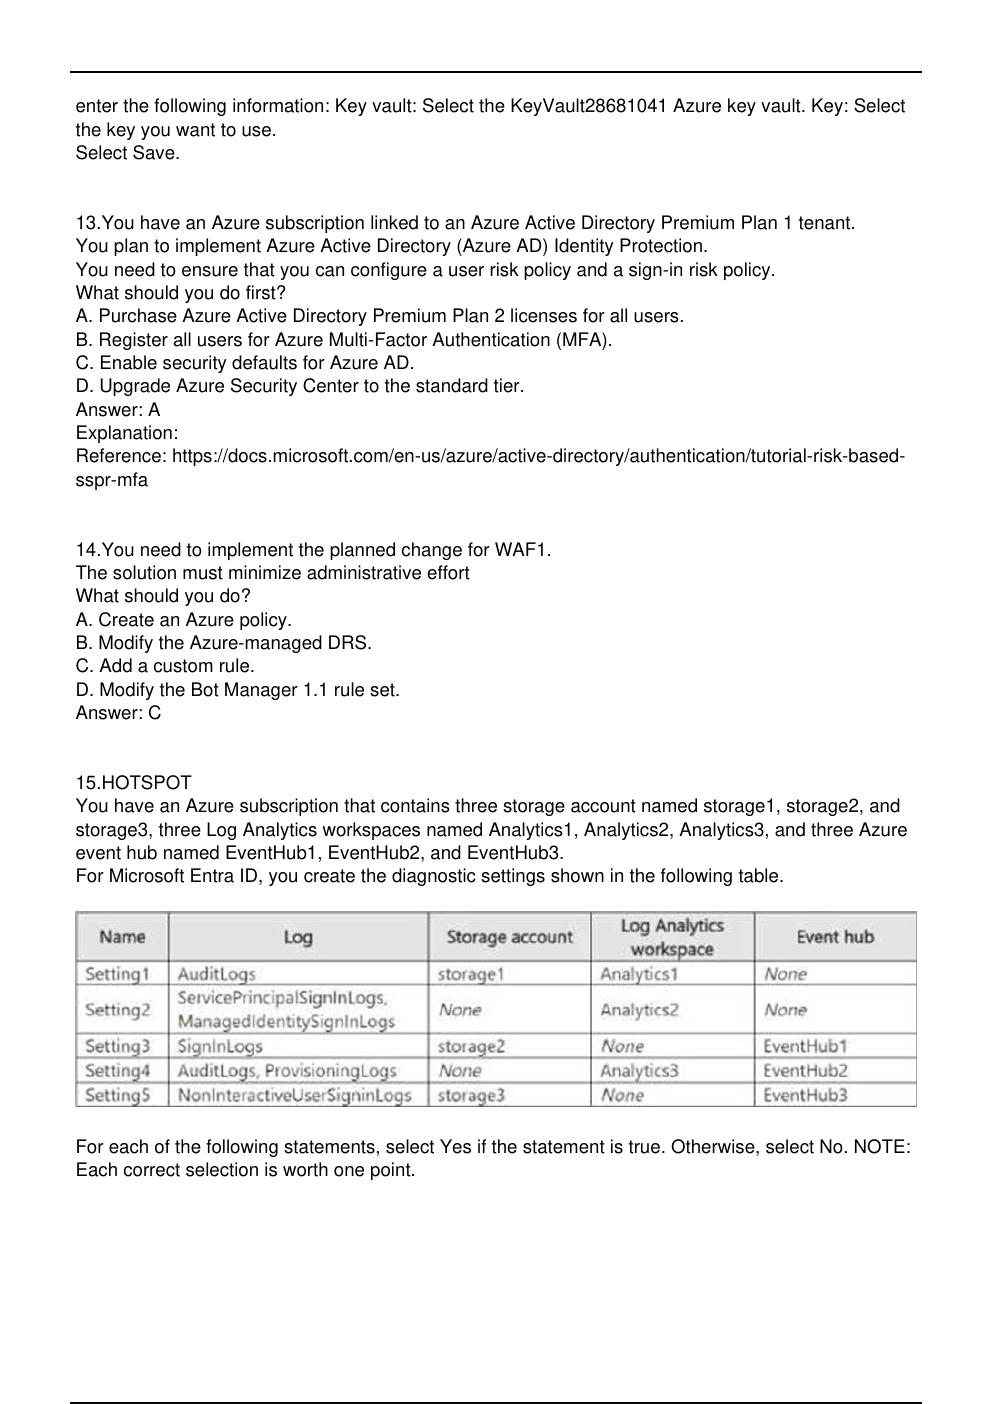
You have an Azure subscription that contains three storage account named storage1, storage2, and
storage3, three Log Analytics workspaces named Analytics1, Analytics2, Analytics3, and three Azure
event hub named EventHub1, EventHub2, and EventHub3.
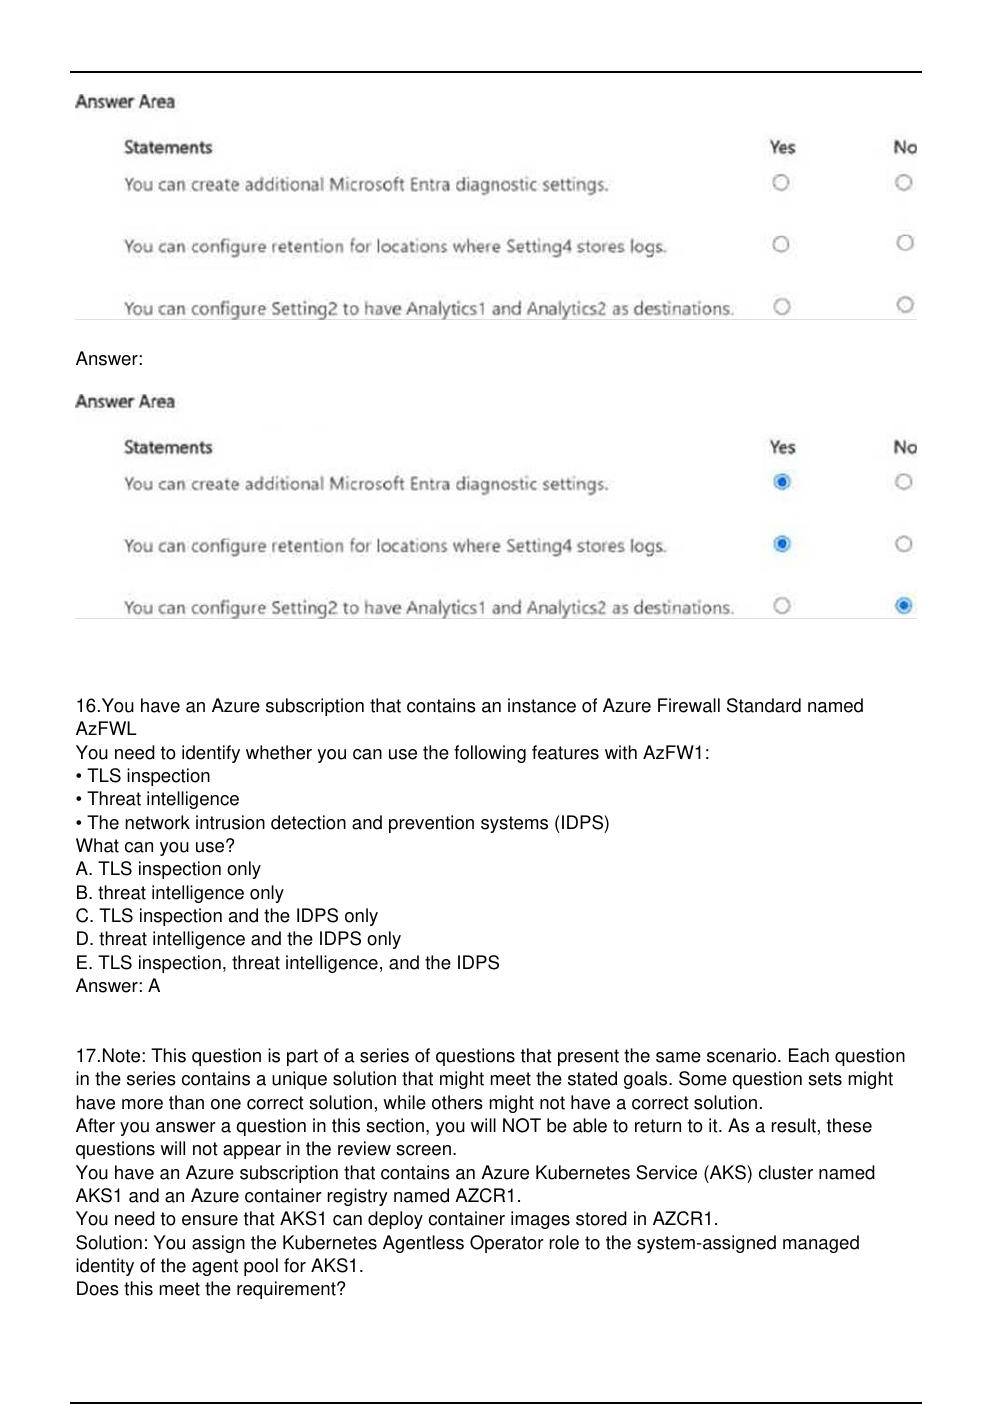
For Microsoft Entra ID, you create the diagnostic settings shown in the following table.
For each of the following statements,